Tenable Nessus · .nessus XML export
Nessus vulnerability reports
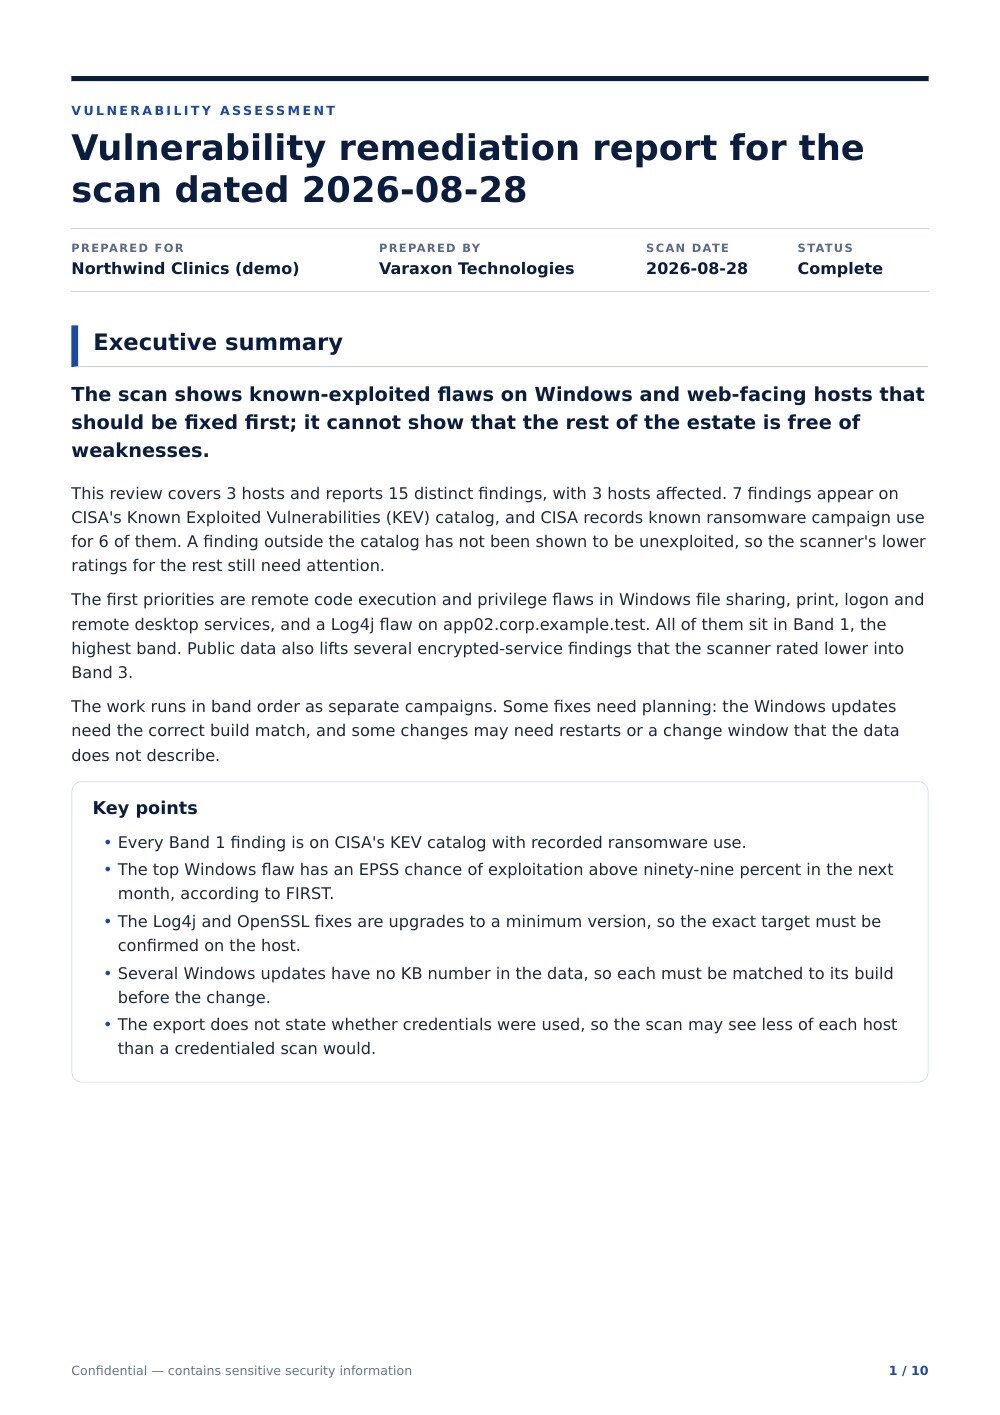
Upload a .nessus XML export and Varaxon Scan Hub produces a structured report from the findings, hosts, plugin metadata and CVE references the export actually contains.
What the export provides
Structured CVE references.
Nessus exports normally carry CVE identifiers per finding, so CVE-based assessment is usually available without any enrichment step.
Plugin identifiers and output.
Plugin IDs, names and scanner output are preserved so each conclusion traces back to evidence.
Host and service context.
Findings stay attached to the host and service the scanner observed them on.
What the report states explicitly
- Where a finding carries no CVE reference, the CVE set is reported as Unknown.
- Where one scan yields two different CVE sets for the same plugin, the finding is quarantined and both variants are kept.
- Coverage limits are written into the report rather than left to interpretation.
Guide
How to read a Nessus scan reportWhat each severity, plugin and output field means, and how to turn it into a client report.Read the guideComparing scanner families? See how Greenbone / OpenVAS exports are handled.